Business Impact Analysis: Meaning, Metrics and IT Recovery
A business impact analysis shows what would stop first if your office lost a key system. The useful result is a short, owned record for recovery.
A business impact analysis shows what would stop first if your office lost access to a key system, site or supplier. It links that disruption to customer service, cash flow and the time your team can wait for recovery. For a Dubai office, the useful result is a short, owned record that guides recovery, not a form that sits untouched.
What a business impact analysis examines
A business impact analysis (BIA) identifies the work your organisation must keep running, then estimates what happens when that work is disrupted. It connects each key activity to the people, systems, records and suppliers it needs. The aim is to set recovery priorities using business impact, rather than whoever shouts loudest during an outage.
Start with activities, not hardware. In a small Dubai office, these might include responding to client requests, issuing invoices or paying staff. Then ask what each activity depends on. A team may need its cloud accounting system, a working internet link and access to a shared folder. If one person holds the only admin login, that person is also a dependency.
For each activity, record how the impact changes over time. An hour without email may be manageable. A full day without access to client records could delay work and damage trust. Use your own figures to estimate financial impact, then capture non-financial harm such as missed commitments or exposure of important records.
A useful BIA has clear outputs. Record the activity owner, impact over time, recovery targets and resource needs. Include the agreed priority order and the date for the next review. A small-business cybersecurity checklist for Dubai offices can help you examine whether protection and backup arrangements match the systems your teams rely on.
Keep the analysis separate from related work. A risk assessment asks what could go wrong and how likely or serious it may be. A BIA asks what a disruption would do to the business. Business continuity planning sets out how people keep priority work going; disaster recovery focuses on restoring IT services and data. The BIA helps connect those plans to agreed business needs.
For a small firm, the report needn't be long. It should include a short summary, the method used, key findings and recommended actions. Add the owner for each action. If a reader can't tell who decides a priority or checks a restore, the document needs more work.
How disruption affects operations, customers and revenue
Disruption usually spreads through dependencies. Imagine your office internet link fails before a client deadline. Staff can't reach cloud files, the team can't send the finished work and the manager can't confirm when service will resume. The initial fault is technical. The impact is delayed work and a customer left waiting.
That chain is why a BIA should look beyond direct costs. Revenue may stop while a sales or payment system is down. Staff may spend hours switching to manual work. A late invoice can delay cash coming in, while a missed service commitment may put a client relationship at risk. Note each effect separately instead of hiding them under a single label such as business impact.
Time matters. Ask process owners what would happen after a short outage, later that day and after several days. The right intervals depend on the work. Payroll, customer response and monthly reporting don't all have the same deadline. Use a known busy period too, such as month-end invoicing, if losing access then would cause a different impact.
Use evidence where you have it. A manager can estimate the value of delayed work from sales or billing records, then check that estimate with finance. For service impact, ask what commitments are affected and who needs to be told. A survey report on UAE small and medium-sized businesses is available; your own BIA should still use your organisation's data to judge the cost of an outage.
Disruption can also expose a gap that was easy to miss on a normal day. If a staff member leaves and nobody else can access a key cloud account, a routine handover becomes a service interruption. If a supplier changes its system, a process may fail even though your own network is healthy. Record workarounds and the limits of each one. A spreadsheet may keep a task moving for a few hours, but it may not preserve a clear audit trail or prevent duplicate entries.
Listonics works with office networks, workstations, cloud accounts, security and backups. That mix is relevant when you map a process to the systems that support it. The BIA should still be owned by the business. IT can explain the dependencies, but process owners and management decide how much delay the organisation can accept.
MTD, RTO and RPO: three recovery measures with different jobs
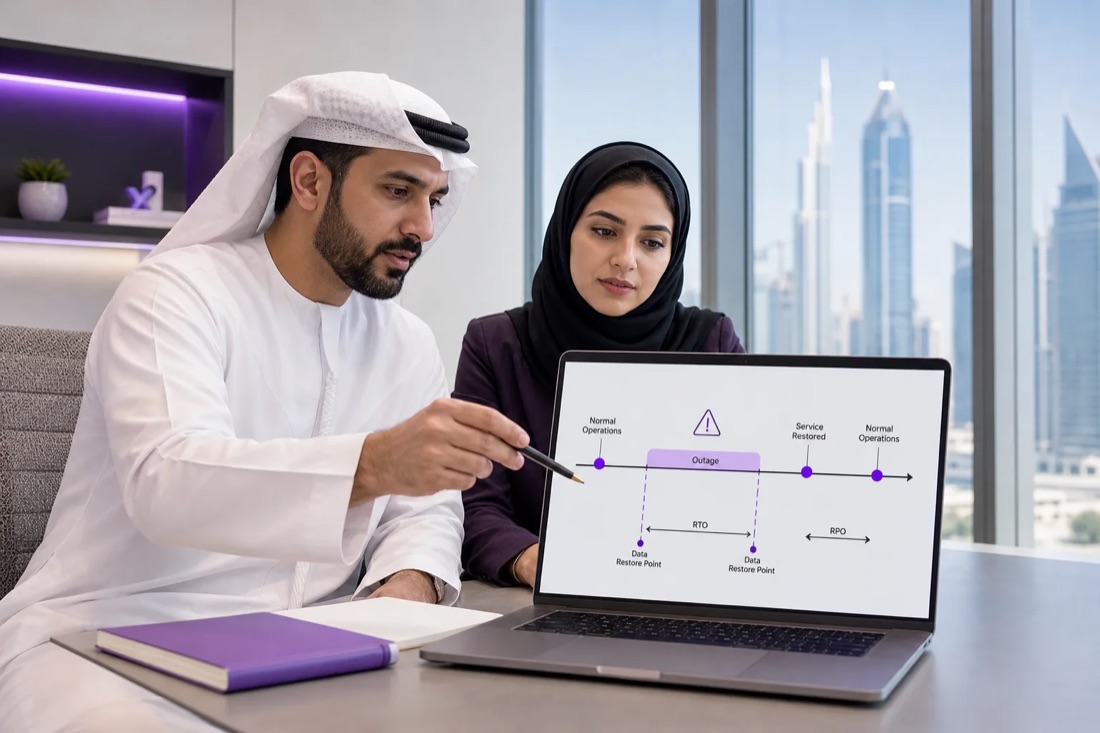
These three measures answer different questions. Maximum tolerable downtime (MTD) is the longest a business activity can remain disrupted before the impact becomes unacceptable. Recovery time objective (RTO) is the target time for restoring the service or system that supports it. Recovery point objective (RPO) is the amount of recent data the business can afford to lose.
- MTD: How long can the business tolerate the activity being unavailable?
- RTO: How soon should the system or service be restored?
- RPO: How far back might restored data go, based on the last recoverable copy?
RTO normally needs to be shorter than MTD, so recovery can happen before the business reaches its limit. RPO is about data loss, not outage length. Mixing it with downtime can lead to a plan that sounds precise but doesn't say whether a team can resume work or how much recent information may be missing.
Say your team can only tolerate a short period without access to client files. Its RTO should reflect how quickly that service needs to return. The RPO should reflect whether the team can recreate work entered since the last backup. Those targets may differ by system. A shared folder with active client work may need a tighter data-loss limit than an archive that changes rarely.
Targets have a cost. Faster recovery can need different systems, backup arrangements or staff cover. Set the target from the impact first, then ask what it takes to meet it. A structured BIA process can help document analysis; Dubai businesses should adapt the questions to their own operations and local setting.
Don't set every system to the fastest possible target. That may cost more than the business impact justifies. Instead, agree which activity needs quick recovery and what level of data loss it can accept. Then ask the IT team to show how those targets can be tested.
How a BIA establishes recovery priorities and dependencies
A recovery priority hierarchy says what needs to return first when several things fail at once. It should come from process criticality, outage impact, tolerable downtime and the resources needed to recover. If you skip the first part and start with a list of servers, the order is a technical guess, not a business decision.
Map each priority activity to its dependencies. Include the systems, equipment and records it needs, along with the staff who can perform the work. Note key suppliers and the facilities required. For a small office, a single cloud account or person with admin access can matter as much as a server. A plan that ignores that dependency can't work as written.
Use a short questionnaire with process owners. Ask what work must continue, what stops it and what a workable fallback looks like. Then ask what evidence supports the requested recovery time. A client deadline, payroll date or service commitment gives a target more weight than a general claim that a process is critical.
Take care with that word. If every activity is marked critical, the team has no useful order and may be unable to fund every recovery target. Rank work by impact over time. Some tasks can pause briefly; others may need a manual fallback while systems are restored.
Write down the decisions. A helpful record names the process owner, the agreed priority and any open dependency that needs action. Include a deputy where one person holds key knowledge. If the office uses a cloud system, record how the business can reach its account and who can approve access during an incident. For software choices, questions about data ownership and export rights can help you assess whether you can retrieve records if a supplier or service changes.
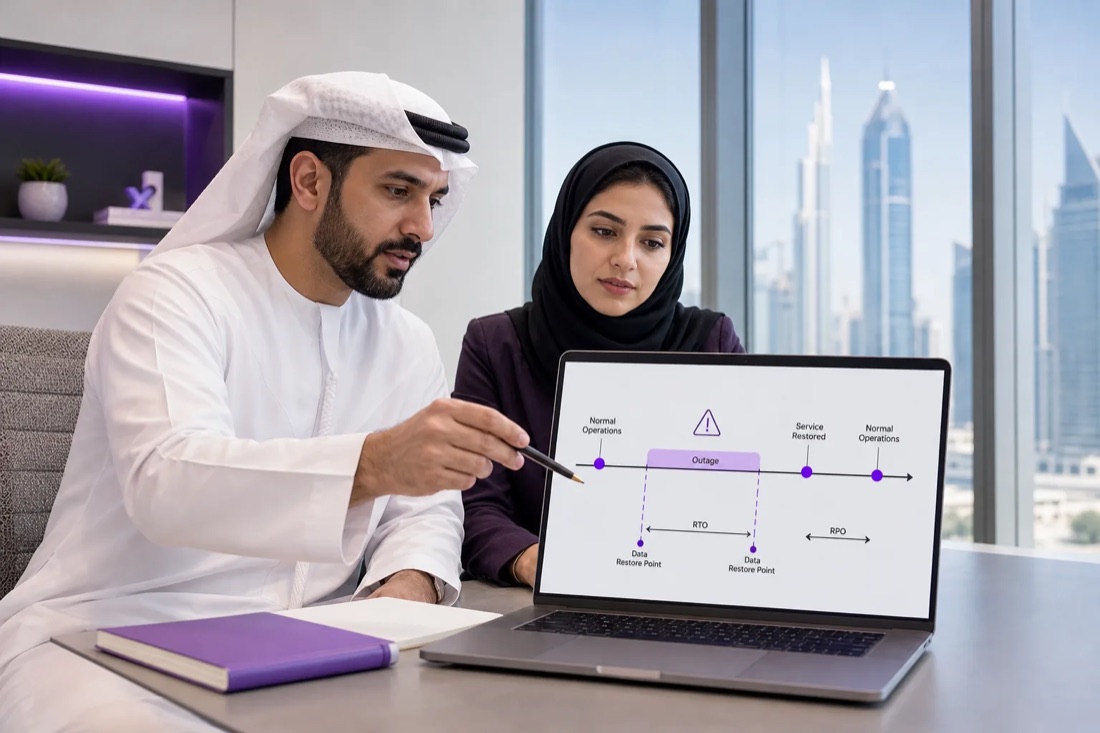
Many checklists name activities but leave the deliverable, owner or review date vague. Ask for a BIA report, a priority hierarchy and a list of actions with named owners. Assign one person to keep the record current. Review it at least once a year as a sound operating habit, and sooner after a major change to systems, suppliers, staffing or office setup.
From BIA findings to tested IT recovery
A BIA is useful only when its findings shape the recovery plan. Turn each priority into a response: prevent the failure where that is sensible, use a workaround if one exists, then restore the system or data within the agreed target. The order depends on the activity, not on which device is easiest to reboot.
For example, if client work depends on cloud files, the plan should say who can restore access and where the backup is held. It should also state how staff will handle urgent requests while access is down. A backup job marked successful is not proof that the files can be restored. Test a restore and record what came back, how long it took and what needs fixing.
Check the full chain. A restored system may still be unusable if staff can't sign in, a firewall blocks the connection or a supplier's service remains down. Recovery testing should include the people and access needed to resume work. Keep the result beside the target, so the business can see whether the plan met its aim.
Listonics designs, installs and manages office IT infrastructure in Dubai, with on-site service across the UAE and remote support. For a small office, documented scope and response times help make ownership clear. Go-live should include the handover of records and the start of ongoing support, not just the moment equipment is switched on.
Keep the final report readable. A manager should be able to find the summary, method, priority findings and recommended actions without searching through technical notes. Add a name and due date to each action. Review the document after tests, incidents or significant changes, then update the recovery plan to match what the test showed.
That distinction matters: an objective is a target, while a test provides evidence. If a restore takes longer than the agreed RTO, change the recovery method, the target or the resources behind it. Don't leave a target in the document simply because it looks good.
Recovery is not a separate topic from security. The NIST Cybersecurity Framework treats recover as one of its six core functions, alongside govern, identify, protect, detect and respond, and the CISA #StopRansomware Guide recommends keeping offline, encrypted backups and testing them regularly. A BIA tells you which systems those tests should cover first. If backup is the weak point your BIA exposes, see how we set up office backups in our NAS storage and backup service.
Conclusion
Keep your analysis short, owned and tied to tested recovery targets. Start by asking process owners what must keep working, then map the systems and people behind it. If you're reviewing office IT alongside continuity, Listonics' network security guide for small businesses in Dubai is a useful next read.
Frequently asked questions
A business impact analysis identifies how disruption affects your organisation's key activities. It links each activity to its systems, people and other dependencies, then records the impact of downtime. The findings help managers set recovery priorities and agree targets for restoring services and data.
A BIA looks at the effect of disruption on business activities. A risk assessment considers potential threats and how they may affect the organisation. Use the risk assessment to understand what could happen; use the BIA to decide what must recover first and how quickly.
Review it at least annually as a sensible management routine, and update it sooner when a major change affects your work. A new cloud system, supplier, office or key role can change dependencies. Also review the analysis after a recovery test or incident reveals that an assumption was wrong.
A named business owner should be accountable for keeping the BIA current, with process owners confirming their activity details. IT can map systems and recovery options, but it shouldn't set business tolerance on its own. For a small office, one manager may coordinate the record and ask each owner to check their section.
Test it. Restore the relevant data or service, measure the time and check whether staff can resume the priority activity. Compare the result with the RTO and RPO. If the test misses either target, record the gap and agree whether to change the recovery plan, the resources or the target.
Written by Srinivasan Ramachandran, Founder, Listonics · Published Oct 15, 2026 · Last reviewed October 28, 2026 · 2132 words